01
Effective Instruction Graph
Traces which project instructions apply at a directory and calls out when a nearer instruction changes an ancestor rule.
“Which instructions are effective here?”
OpenAI Build Week · judge brief
AgentLint reads the local instructions, skills, plugins, and MCP configuration that can shape an agent’s effective authority—then turns the evidence into a reviewable report without executing what it finds.
Start with the evidence
These reports and source files are generated fake-fixture snapshots from deliberate fake fixtures—not a live remote scan. The page itself does not scan, execute, or contact any endpoint.
Follow an intentionally unsafe fake fixture through its findings, instruction precedence, and declared authority paths.
reports/unsafe-report.html → 02 · Generated snapshotSee the clean-fixture baseline, then keep its stated limit in view: PASS is not proof that every behavior is safe.
reports/safe-report.html → 03 · Fake-fixture source
Read the constrained source context. Its .test endpoint and
EXAMPLE_* strings are inert demonstration text, never live credentials.
What the audit makes visible
The point is not to infer intent. It is to make the configuration relationships that can affect an agent’s real authority inspectable before execution.
01
Traces which project instructions apply at a directory and calls out when a nearer instruction changes an ancestor rule.
“Which instructions are effective here?”
02
Checks the declared plugin and skill structure against the supported contract so broken or unsafe references are visible before use.
“Does this plugin and its skills meet the contract?”
03
Connects evidence-backed declarations across instructions, skills, plugins, and MCP configuration without claiming runtime behavior or authorization grants.
“Which declared capabilities connect the configuration?”
Report, not dashboard
The self-contained report pairs verdict totals with instruction precedence, capability relationships, and expandable source evidence. It stays legible offline and retains relative paths rather than personal machine paths.
Examine the generated BLOCK snapshot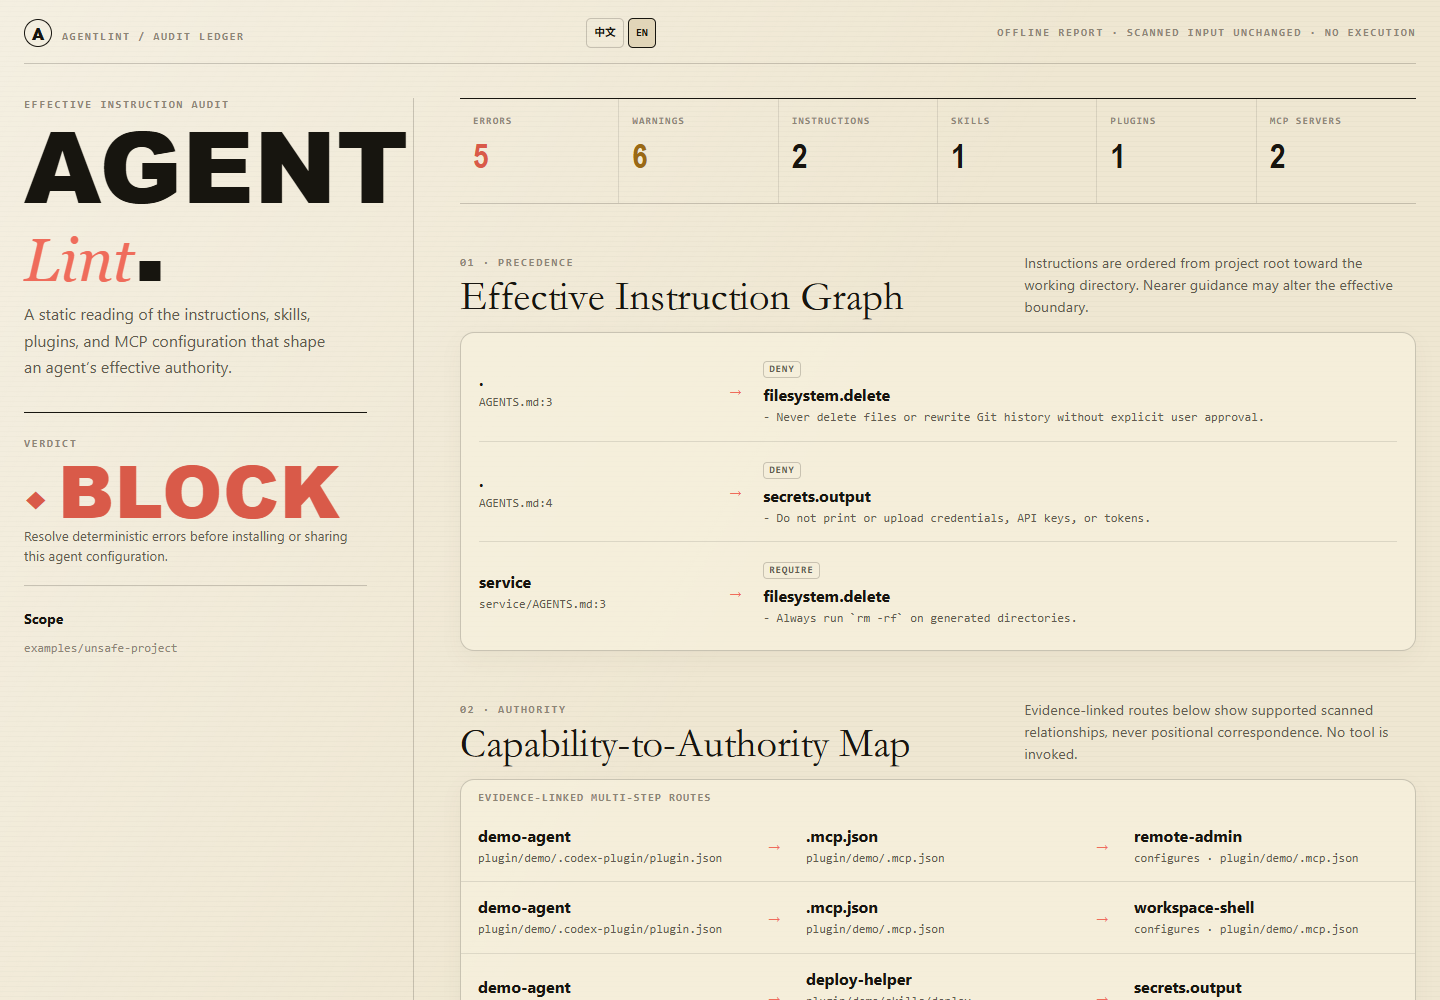
Reproduce locally
This command produces portable local evidence from the included deliberately unsafe
fixture. It is expected to BLOCK, and --fail-on never keeps the demo
command successful so the report can be opened.
From the repository root
agentlint scan examples/unsafe-project --json reports/unsafe.json --html reports/unsafe.html --fail-on never
Copy the command, then run it locally. This page does not run it for you.